eBook INGLÉS EPUB sin DRM
API SECURITY
Authentication, authorization, rate limiting, and defence for the modern API surface.
Por IMAD MURATSPAHIC
Nuevo
-5% de dto. exclusivo web
Sinopsis
API Security is the definitive practical engineering guide to securing the interface layer of modern software. It starts from a single observation: the API is where the business logic runs, where the data lives, and where every external actor enters the system — and the specific ways that APIs fail under adversarial pressure are well-documented, well-understood, and still routinely exploited. The book walks through the full discipline — why API security matters and why the API surface has become the primary attack surface of modern systems, the OWASP API Top 10 and the specific attack patterns for each category, authentication fundamentals and the trade-offs between API keys and mTLS and token-based auth, OAuth 2.0 and OpenID Connect with the correct implementation of each flow, JWTs and the specific vulnerabilities that algorithm confusion and weak keys introduce, session management and the cookie attributes that make browser-based auth secure, authorization models from RBAC to ABAC to ReBAC, Broken Object-Level Authorization — the number one API vulnerability — and the systematic testing that catches it, rate limiting algorithms and the dimensions that determine which abuse patterns each catches, input validation and the injection defences for SQL, NoSQL, LDAP, command, and template injection, API gateways and the configuration patterns that make edge controls effective, API observability and the detection patterns that catch attacks in progress, API incident response and the coordination that a multi-client API demands, and the trends reshaping the field. It covers the failure modes that quietly wreck API security: a BOLA vulnerability that exposes every customers data through a single missing check, a JWT accepted after the user has been deactivated because the token has not expired, a redirect URI validation that accepts any subdomain, a rate limit bypassed through distributed IPs, a scope definition that grants access to every resource when only one was intended, a mass assignment vulnerability that allows an attacker to set is_admin on their own account, an audit log that misses the specific event an investigation needs. Each is presented with the failure, the countermeasure, and the operational tradeoff.
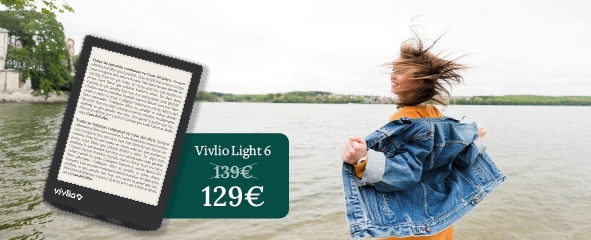
eReader Vivlio Light 6 con 10 € de descuento
Disfruta de tus lecturas este otoño con el eReader Vivlio Light 6 y ahorra 10 €. Oferta válida hasta el 5 de octubre o hasta agotar existencias (250 unidades).
Léelo en cualquier dispositivo


Ficha Técnica
Editorial: Muratspahic Imad
ISBN: 9789910063121
Idioma: Inglés
Fecha de lanzamiento: 21/09/2026
Especificaciones del producto
Reseñas sobre API SECURITY (EBOOK)
Comparte tu experiencia con la comunidad lectora.
0 Reseñas
5 0
4 0
3 0
2 0
1 0
Sólo por opinar entras en el sorteo mensual de tres tarjetas regalo valoradas en
20€
Publicar una opinión supone haber leído y aceptado las
bases del sorteo
"Tu opinión tiene premio".